Updated 2026 · 10 min read
Table of Contents
1-What’s Actually Going On Here
2-The Fastest Fixes First
3-Why This Happens
4-The IPv6 Problem Almost Nobody Checks
5-Full Fix List
6-Protocol Matters More Than People Realize
7-When Its Not DNS: Other Causes to Rule Out
8-Final Thoughts
9-Asked Questions
10-Whats Actually Going On Here
Overview
A VPN showing as connected while every website fails to load is a specific and confusing state. The app thinks everything is fine but no actual traffic is getting through. The connection icon is green the timer is counting up the server name is displayed like normal and yet every tab just spins or times out. It’s a problem from the VPN failing to connect at all and its worth treating it that way because the fixes for a stuck connection attempt and a “connected but useless” tunnel are almost entirely different.
The Fastest Fixes First
Flushing DNS after connecting has become a habit for me now since this exact issue is always a DNS problem rather than the VPN connection itself. On Windows that means running ipconfig /flushness in Command Prompt; on Mac it’s do ds cache util -flush cache; sudo kill all -HUP m DNS Responder in Terminal. Do this after connecting then try loading a site again before touching anything else.
If that doesn’t help immediately switch to a VPN server in the same app. The server you’re connected to may have a healthy tunnel but a broken route to the wider internet. This happens more often with overloaded or less-maintained server locations than people expect.
Why This Happens
This typically points to one of these causes:
-DNS resolution failure through the VPN tunnel specifically. The tunnel carries traffic fine. The DNS server its routing requests to isn’t responding
-A routing conflict between the VPN and your local network, especially common on networks with unusual subnet configurations
-An outdated VPN app, which can carry unresolved routing bugs tied to specific server configurations
-The VPN server itself being connected but unable to reach the wider internet, which is a server-side problem rather than anything on your device
-IPv6 traffic bypassing or conflicting with the VPN tunnel, which is increasingly common as more networks default to IPv6 alongside IPv4
-The IPv6 Problem Almost Nobody Checks
This is one of the overlooked causes in 2026 as IPv6 has become the default on a growing number of home networks and ISPs. Here’s the issue: many VPN apps only fully tunnel IPv4 traffic by default while your device may still be trying to reach websites over IPv6 outside the tunnel. When that happens DNS requests or connection attempts go out over IPv6 hit your non-VPN) network path and either fail outright or get blocked by the same network-level restriction the VPN was supposed to get around in the first place. While the VPN app itself shows a perfectly healthy IPv4 tunnel the whole time.
The fix is usually one of two things: enable “IPv6 leak protection” or a named setting in your VPN app if it has one or disable IPv6 entirely at the network adapter level on your device while connected to the VPN. Most major VPN apps added IPv6 handling by now but plenty of routers, smart TVs and older app versions still don’t manage it cleanly which makes this a genuinely common cause of exactly this symptom.
Full Fix List
1-Flush your DNS after connecting. Run ipconfig /flush dns (Windows) or the Mac/Linux equivalent then reload a page.
Credit :StrongVPN
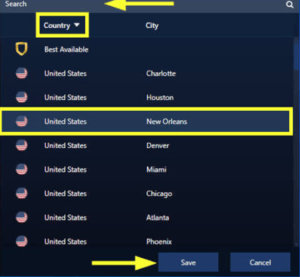
2-Switch VPN servers. A specific server can have a working tunnel but a broken route to the internet.
3-Re-enable the VPN connection. This resets the tunnel state. Often clears a stuck routing table entry.
4-Check your VPN apps DNS settings. Manually setting a known-working DNS server (like an one) instead of the default can bypass a failing resolver.
5-Update the VPN app. Outdated versions can carry routing bugs to certain servers or network types that later updates fix.
6-Run a DNS leak test. Free tools designed for this show which DNS servers your traffic is actually using while connected. If it shows your ISPs DNS instead of the VPNs that confirms the tunnel isn’t properly routing DNS requests.
7-Check for IPv6 leaks specifically using the IPv6 leak protection setting in your VPN app or by disabling IPv6 at the adapter level as a test.
8-Try a VPN protocol if your app offers a choice (see below). Some protocols handle certain network types more reliably than others.
9-Temporarily disable a firewall or antiviruss own DNS filtering to check whether its conflicting with the VPNs routing than the VPN itself being at fault.
10-Protocol Matters More Than People Realize
modern VPN apps let you choose between a few underlying protocols. Commonly WireGuard, OpenVPN and IKEv2. And this choice affects more than just speed. WireGuard has become the default for providers by 2026 because its fast and handles reconnections cleanly but it can occasionally have rougher edges on networks with strict or unusual firewall rules since its a comparatively newer leaner protocol. OpenVPN while slightly slower tends to be more tolerant of restrictive or unusual network setups precisely because its been around longer and has more mature fallback behavior built in.
If you’re stuck on “connected but nothing loads”. None of the DNS-focused fixes have worked, switching your apps protocol setting from its default to an alternative is worth trying before assuming the server itself is broken. This is a setting that exists in every mainstream VPN app now but sits buried in advanced or connection settings so people rarely know to look for it.
When Its Not DNS: Other Causes to Rule Out
If DNS flushing server switching and protocol changes all fail to help a less common causes are worth ruling out:
Split tunneling misconfiguration. If you’ve set specific apps or sites to bypass the VPN, a misconfigured rule can accidentally route everything outside the tunnel or conversely trap traffic that should be excluded
A kill switch stuck in a false-triggered state. Some VPN apps include a kill switch that blocks all internet traffic if it detects the tunnel dropped and occasionally this can get stuck “on” even after the tunnel reconnects successfully
Router-level VPN conflicts if you’re running the VPN at the router level rather than per-device since a misconfigured router VPN client can create routing loops that individual device troubleshooting won’t fix
MTU size mismatches, a more technical cause where the VPN tunnels packet size setting doesn’t match what your network path actually supports causing packets to silently fail rather than generating an obvious error
Final Thoughts
DNS problems explain this exact combination of symptoms more often than any other cause since the VPN tunnel itself can genuinely be connected while DNS resolution through it fails silently. Flushing DNS and switching servers together resolve the majority of cases without needing to reinstall anything. If that doesn’t clear it up checking for an IPv6 leak and trying a protocol are the next two most useful things to try before assuming something deeper is broken.
Frequently Asked Questions
Why would the VPN show as connected if nothing actually works?
The VPN app confirms the tunnel connection itself which’s a separate step from DNS resolution and general internet routing working correctly through it. The app has no way of knowing DNS is failing unless it specifically checks for that.
Does this mean my VPN providers servers are down?
Not necessarily. It’s often a DNS or routing issue specific to the server you’re connected to which switching servers usually resolves without needing to contact support.
Can antivirus software interfere with VPN DNS resolution?
Yes some security software includes its DNS filtering that can conflict with a VPNs routing. Temporarily disabling it helps confirm this as the cause before making any permanent changes.
What’s a DNS leak test. Do I actually need one?
It’s an online test that shows which DNS servers your device is actually using while connected to a VPN. It’s worth running if this issue happens repeatedly since it gives you an answer rather than a guess.
Is IPv6 really likely to be the cause for me?
It’s more likely than it used to be on newer routers and ISPs that default to IPv6. If your VPN app has an IPv6 leak protection toggle and its off that’s worth checking rather than last.
Should I switch protocols permanently or just to test?
Just to test, at first. If a different protocol consistently fixes the issue on the networks you use most it’s reasonable to leave it set that way. Theres no universally “best” protocol, for every situation.
About This Guide
I ran into a version of this myself after switching internet providers to one that defaulted to IPv6. The VPN showed connected the time and it took a DNS leak test to actually confirm what was going wrong before enabling IPv6 protection fixed it.
Related Fix:
https://appfixguide.net/vpn-keeps-disconnecting-on-wifi-fix/